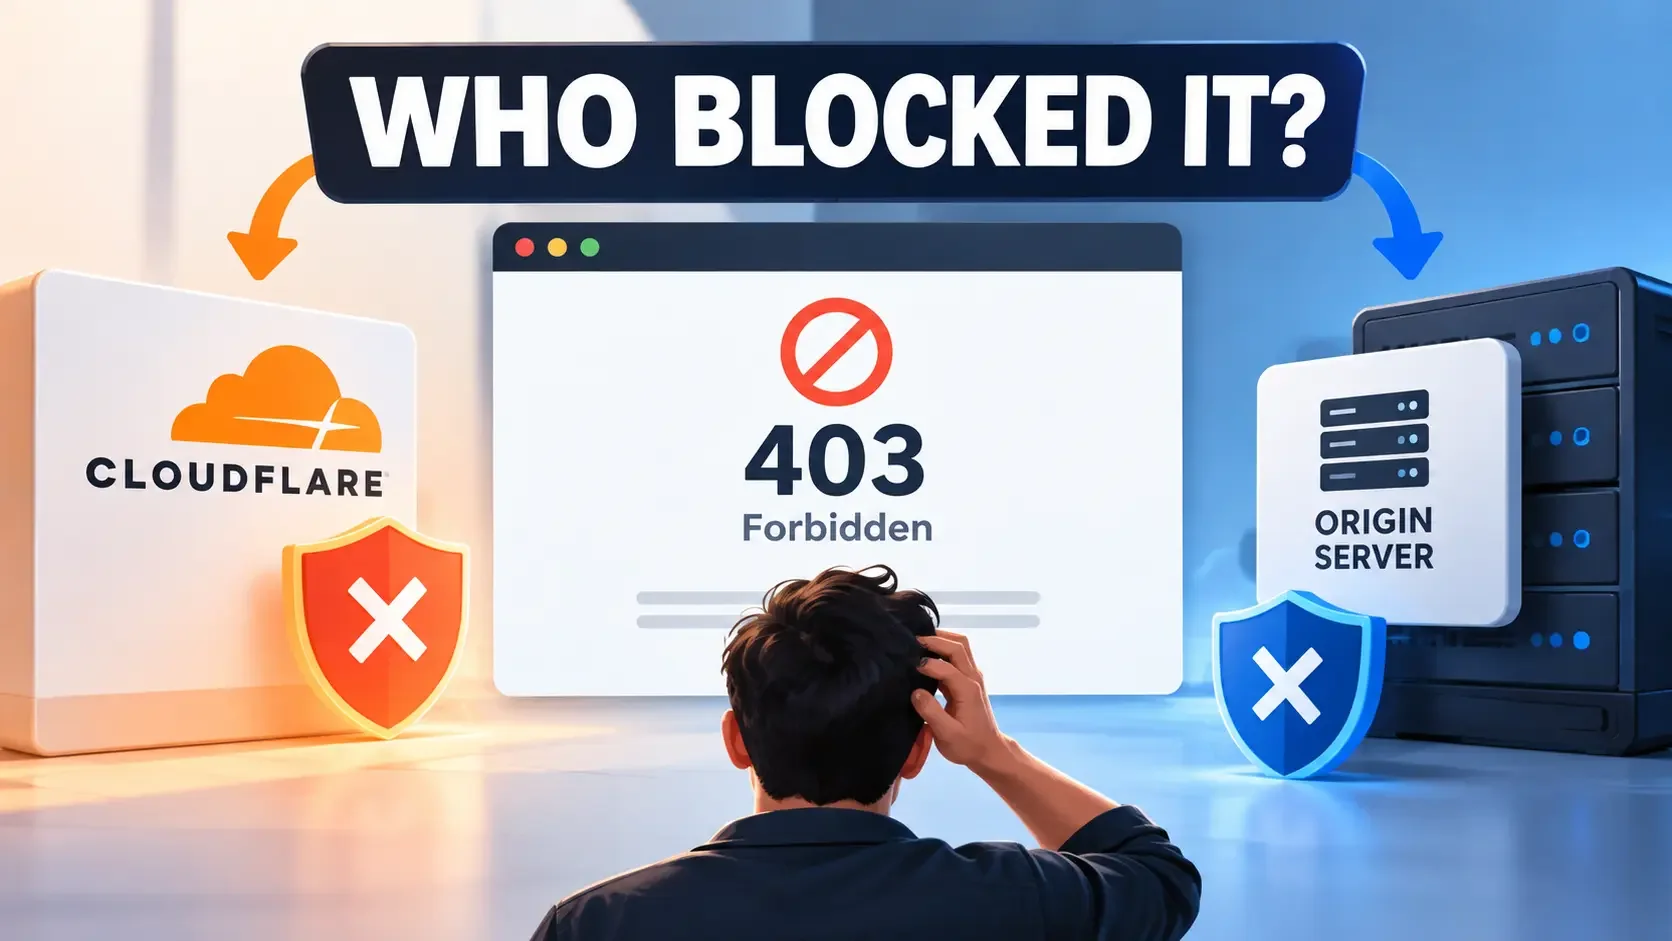
A Cloudflare 403 Forbidden error does not necessarily mean Cloudflare blocked your request. The website's origin server might have rejected it or Cloudflare might have stopped the request before it ever reached the server.
The difficulty is that these different failures can produce nearly identical error messages. To find out who actually blocked the request, you need to establish where the rejection occurred rather than relying on the HTTP status alone.
I would investigate three pieces of evidence: the response Cloudflare delivered, any matching Cloudflare security event and the response recorded from the origin server. Together, these can distinguish a Cloudflare security block from an origin-level denial without making unnecessary configuration changes.
First Clue Is the 403 Response Itself
Cloudflare's official documentation makes an important distinction between branded and unbranded 403 responses. A Cloudflare-branded block page generally indicates that one of its security features intervened, while an ordinary unbranded 403 typically points toward the origin server.
However, Cloudflare also documents exceptions where its infrastructure returns an unstyled 403 before the website's security configuration loads. That means the appearance of the page is useful evidence but it should not be treated as a final diagnosis.
| What the visitor sees | Initial interpretation | Evidence needed |
|---|---|---|
| Cloudflare-branded 403 | Likely Cloudflare security enforcement | Matching Security Event |
| Error 1020: Access denied | Cloudflare security feature blocked the request | Responsible feature and rule |
| Plain 403 Forbidden | Usually the origin server | Origin response and server logs |
| Application-specific permission message | Likely application authorization | Application log entry |
| Unstyled 403 with no security event | Origin rejection or early Cloudflare processing | Origin logs and connection details |
The distinction becomes particularly important when a website uses more than one security system. A request can successfully pass Cloudflare's protection and still be rejected by the hosting firewall or application.
My assessment is that the error page should determine the starting point of an investigation, not the conclusion.
Find the Request in Cloudflare Security Events
When a Cloudflare-branded page reports that access was denied, the Cloudflare Ray ID is usually the most useful identifier to collect. It may appear on the error page itself or in the failed request's cf-ray response header.
You can inspect that header through your browser's Developer Tools by opening the Network tab and selecting the affected request. Record the Ray ID alongside the exact URL and the time the error occurred.
Cloudflare assigns Ray IDs to requests passing through its network but those identifiers are not guaranteed to be globally unique. The hostname and timestamp therefore provide additional context when matching an error to a particular request.
Identify the security feature that blocked the request
Website administrators can open the Cloudflare dashboard, select the affected domain and navigate to the Analytics page's Events tab. The Security Events records can identify requests that Cloudflare security products acted on or flagged.
Set a narrow time range around the failed request and filter by Ray ID where supported. If necessary, use the client IP address and other request details to narrow the search.
A matching event can reveal whether the request triggered a managed WAF rule, a custom rule or another Cloudflare security feature. The recorded action is important because an event that merely logged suspicious activity is different from one that actually blocked the request.
For example, suppose a legitimate API request returns 403 and its matching event identifies a managed rule with a Block action. That provides strong evidence that Cloudflare's security layer denied the request.
The remaining question is whether the rule correctly identified unwanted traffic or mistakenly blocked an expected application request. Identifying the responsible rule does not automatically mean that the rule should be disabled.
When no matching security event appears
An empty search result does not prove that Cloudflare allowed the request. Cloudflare states that Security Events can use sampled data, meaning individual requests may be missing from the displayed records.
Reducing the time range can improve the investigation, but some early Cloudflare rejections are not recorded in the normal security event history. When no event is found, I would leave the cause unconfirmed until the origin response has also been examined.
Compare Cloudflare and Origin Responses
This is where the investigation becomes more reliable than simply interpreting an error page.
Cloudflare acts as a reverse proxy, meaning that it can receive the origin server's HTTP response and deliver that response to the visitor. Consequently, a browser may receive a 403 through Cloudflare even when the rejection originated entirely from the website's server.
Where detailed Cloudflare HTTP request logs are available, two fields help separate these possibilities.
| Log field | Meaning |
|---|---|
EdgeResponseStatus | HTTP status Cloudflare returned to the visitor |
OriginResponseStatus | HTTP status recorded from the upstream server |
Cloudflare documents these fields in its logging system. Their availability depends on the account's logging capabilities and configuration.
When the edge and origin both return 403
Consider a request with EdgeResponseStatus = 403 and OriginResponseStatus = 403.
The record shows that Cloudflare delivered a 403 and also received a 403 response from the upstream server. This makes the origin an important place to investigate because it independently refused the request.
For example, a web application might deny access because a user's role does not permit opening an administrative page. Cloudflare can deliver that response without being responsible for the application permission.
I would look for the corresponding request in the origin logs before changing any Cloudflare security rules.
When Cloudflare returns 403 without an origin response
Now consider a different record: EdgeResponseStatus = 403 and OriginResponseStatus = 0.
This tells us that the log entry does not contain an HTTP response from the origin. However, it does not establish that a Cloudflare WAF rule blocked the request.
Cloudflare documents several circumstances in which no origin response is recorded, including requests served at the edge and situations involving Workers. The cache status and other request-processing details must be considered before attributing the response to security enforcement.
If a matching Security Event also records a Block action, the evidence for Cloudflare security enforcement becomes stronger. Without that event, I would investigate the remaining edge-processing possibilities instead of assuming the firewall caused the error.
Check for Origin Server Blocks
If the request logs show an origin-generated 403, the next step is to identify which origin component rejected it.
Cloudflare's documentation identifies server permission rules, ModSecurity restrictions, and IP-deny configurations among the common causes of unbranded 403 errors. An application can also generate the same status when a user lacks permission to access a particular resource.
The strongest evidence comes from matching the failed request to the origin server's access, error, or security logs. Ideally, those records should identify the affected path, the request time, and the restriction responsible for the denial.
Server Restrictions vs. Application Denials
Suppose a website returns 403 when a visitor attempts to open a protected directory. An Apache access-control rule might be responsible, and the web-server configuration would be the appropriate place to investigate.
Now consider an authenticated customer receiving 403 when opening an account resource. If the application logs show that the customer lacks the required authorization, changing Apache or Cloudflare firewall rules would not resolve that underlying permission issue.
The difference matters because both errors can look identical when delivered through Cloudflare. The origin logs establish which component made the decision.
Hosting Firewall Blocks Cloudflare Traffic
An origin firewall can also block requests arriving through Cloudflare's proxy network. This can happen when the hosting environment incorrectly denies the IP addresses used by Cloudflare.
If the hosting security logs identify this restriction, the administrator should compare the firewall rules against Cloudflare's published IP ranges. The appropriate correction is to address that specific restriction rather than broadly disabling server protection.
A controlled request directly to the origin can help compare its behavior with the proxied request. However, disabling Cloudflare simply to conduct that test can introduce unrelated connectivity problems.
For administrators who actually need to change proxy settings, BusinessTally's guide to disabling Cloudflare without website downtime explains why origin connectivity and certificate readiness should be checked beforehand.
Cloudflare 403 Without a Security Event
There is one important exception to the usual assumption that an unbranded 403 originates from the server.
Cloudflare documents that some requests can be rejected early in its infrastructure, before the website's security configuration has been loaded. Such responses may produce an unstyled 403 and may not appear in normal Security Events.
One documented example involves a mismatch between the HTTP request hostname and the Server Name Indication, or SNI, provided during the TLS connection.
This possibility becomes relevant when investigating custom HTTP clients or proxy configurations that send inconsistent hostname information. It is less useful as an explanation when the request's connection details have not been examined.
I would consider an early Cloudflare rejection when the origin has no corresponding request and the normal security records provide no explanation. Even then, the hostname configuration should be checked before treating the hypothesis as confirmed.
My Assessment of Blocking Evidence
The most useful diagnostic information is not the error code by itself but the combination of request and response records.
Consider the following hypothetical results.
| Investigation result | What I would conclude | Confidence |
|---|---|---|
| Security Event identifies a Block action for the matching request | Cloudflare security blocked it | High |
| Origin log confirms the origin generated HTTP 403 | Origin server or application denied it | High |
| Cloudflare edge returns 403, origin status is 0 and a matching security block exists | Cloudflare security is the likely source | High |
| Plain 403 appears without Cloudflare branding | Origin rejection is likely but not confirmed | Moderate |
| No matching event appears in sampled Security Events | Insufficient evidence to identify the source | Low |
| Request shows an SNI/hostname mismatch consistent with early rejection | Early Cloudflare processing is a strong explanation | High when independently verified |
These assessments are based on the diagnostic evidence each record provides, rather than measurements from a particular production incident.
The important distinction is between proving that a request was denied and identifying the system responsible for denying it.
For example, a Ray ID proves neither that Cloudflare's security rules blocked a request nor that the origin permitted it. A corresponding event with a Block action provides substantially stronger evidence of Cloudflare enforcement.
Likewise, an origin response of 403 establishes that the upstream server returned an access-denied status. The application or web-server logs may then identify the precise permission or rule responsible.
Correct the Block Only After Identifying Its Source
If a Cloudflare security rule caused the rejection, examine the matched rule and the request characteristics before deciding whether an exception is justified. A narrowly scoped exception for legitimate traffic is preferable to disabling an entire security feature without evidence.
If the origin server returned 403, investigate the corresponding web-server restriction, hosting firewall rule or application permission. Changing Cloudflare settings is unlikely to resolve a denial independently generated by the origin.
If the available evidence points toward early Cloudflare processing, inspect the client's TLS and hostname configuration. Correcting an inconsistent request is more appropriate than weakening unrelated website security settings.
For visitors without access to the website's Cloudflare account or server logs, the exact URL, error timestamp and Ray ID are the most useful details to provide to the website administrator. Those details allow the administrator to investigate the responsible system instead of guessing from the displayed message.
A Cloudflare 403 Forbidden response establishes that access was denied but it does not identify who made that decision. The most reliable answer comes from matching the request to a Cloudflare security action, an origin-server rejection or evidence of an early Cloudflare processing failure.